Vulnerability database
Every flaw the U.S. government’s cybersecurity agency (CISA) has confirmed attackers are using, plus the new WordPress plugin and theme bugs published each day, sorted by what they mean for a small business. We refresh it twice a day. If you see something your website or office runs, tell us.
3,394 results · page 33 of 68
Mar 19, 2024UBEE DDW365 XCNDDW365 8.14.3105 software on hardware 3.13.1 allows a remote attacker within Wi-Fi proximity to conduct stored XSS attacks via RgFirewallEL.asp, CVE-2024-28092 · Other software · reported by MITREHigh 7.2
UBEE DDW365 XCNDDW365 8.14.3105 software on hardware 3.13.1 allows a remote attacker within Wi-Fi proximity to conduct stored XSS attacks via RgFirewallEL.asp, RgDdns.asp, RgTime.asp, RgDiagnostics.asp, or RgParentalBasic.asp. The affected fields are SMTP Server Name, SMTP Username, Host Name, Time Server 1, Time Server 2, Time Server 3, Target, Add Keyword, Add Domain, and Add Allowed Domain.
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Mar 19, 2024A multiple Cross-site scripting (XSS) vulnerability in the '/members/moremember.pl', and ‘/members/members-home.pl’ endpoints within Koha Library Management SysCVE-2024-24336 · Other software · koha-community · reported by MITREHigh 8.1
A multiple Cross-site scripting (XSS) vulnerability in the '/members/moremember.pl', and ‘/members/members-home.pl’ endpoints within Koha Library Management System version 23.05.05 and earlier allows malicious staff users to carry out CSRF attacks, including unauthorized changes to usernames and passwords of users visiting the affected page, via the 'Circulation note' and ‘Patrons Restriction’ components.
- Product
- koha_library_software
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordnitipoom-jar.github.ionitipoom-jaroonchaipipat.github.io
Mar 18, 2024RaspberryMatic is an open-source operating system for HomeMatic internet-of-things devices.CVE-2024-24578 · Other software · jens-maus · reported by GitHubCritical 10
RaspberryMatic is an open-source operating system for HomeMatic internet-of-things devices. RaspberryMatic / OCCU prior to version 3.75.6.20240316 contains a unauthenticated remote code execution (RCE) vulnerability, caused by multiple issues within the Java based `HMIPServer.jar` component. RaspberryMatric includes a Java based `HMIPServer`, that can be accessed through URLs starting with `/pages/jpages`. The `FirmwareController` class does however not perform any session id checks, thus this feature can be accessed without a valid session. Due to this issue, attackers can gain remote code execution as root user, allowing a full system compromise. Version 3.75.6.20240316 contains a patch.
- Product
- RaspberryMatic
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Mar 13, 2024A directory traversal within the ‘ftpservlet’ of the FileCatalyst Workflow Web Portal allows files to be uploaded outside of the intended ‘uploadtemp’ directoryCVE-2024-25153 · Other software · Fortra · reported by df4dee71-de3a-4139-9588-11b62fe6c0ffCritical 9.8
A directory traversal within the ‘ftpservlet’ of the FileCatalyst Workflow Web Portal allows files to be uploaded outside of the intended ‘uploadtemp’ directory with a specially crafted POST request. In situations where a file is successfully uploaded to web portal’s DocumentRoot, specially crafted JSP files could be used to execute code, including web shells.
- Product
- FileCatalyst
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordfilecatalyst.softwarefortra.com
Mar 9, 2024Hitron CODA-4582 2AHKM-CODA4589 7.2.4.5.1b8 devices allow a remote attacker within Wi-Fi proximity (who has access to the router admin panel) to conduct a DOM-bCVE-2024-28089 · Other software · hitrontech · reported by MITREMedium 5.2
Hitron CODA-4582 2AHKM-CODA4589 7.2.4.5.1b8 devices allow a remote attacker within Wi-Fi proximity (who has access to the router admin panel) to conduct a DOM-based stored XSS attack that can fetch remote resources. The payload is executed at index.html#advanced_location (aka the Device Location page). This can cause a denial of service or lead to information disclosure.
- Product
- coda-4582u_firmware
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Mar 6, 2024Canarytokens helps track activity and actions on a network.CVE-2024-28111 · Other software · thinkst · reported by GitHubMedium 6.5
Canarytokens helps track activity and actions on a network. Canarytokens.org supports exporting the history of a Canarytoken's incidents in CSV format. The generation of these CSV files is vulnerable to a CSV Injection vulnerability. This flaw can be used by an attacker who discovers an HTTP-based Canarytoken to target the Canarytoken's owner, if the owner exports the incident history to CSV and opens in a reader application such as Microsoft Excel. The impact is that this issue could lead to code execution on the machine on which the CSV file is opened. Version sha-c595a1f8 contains a fix for this issue.
- Product
- canarytokens
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Mar 5, 2024An issue in Jeewms v.3.7 and before allows a remote attacker to escalate privileges via the AuthInterceptor component.CVE-2024-27764 · Other software · erzhongxmu · reported by MITRECritical 9.8
An issue in Jeewms v.3.7 and before allows a remote attacker to escalate privileges via the AuthInterceptor component.
- Product
- jeewms
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Mar 5, 2024The ParseAddressList function incorrectly handles comments (text within parentheses) within display names.CVE-2024-24784 · Other software · Go standard library · reported by security@golang.orgHigh 7.5
The ParseAddressList function incorrectly handles comments (text within parentheses) within display names. Since this is a misalignment with conforming address parsers, it can result in different trust decisions being made by programs using different parsers.
- Product
- net/mail
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Mar 4, 2024Stored XSS Vulnerability in M-Files Web versions before 23.8 allows attacker to execute script on users browser via stored HTML document within limited time perCVE-2023-4479 · Other software · M-Files Corporation · reported by security@m-files.comHigh 7.3
Stored XSS Vulnerability in M-Files Web versions before 23.8 allows attacker to execute script on users browser via stored HTML document within limited time period.
- Product
- M-Files Web
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordempower.m-files.comproduct.m-files.com
Mar 3, 2024As a default user on a multi-user instance of AnythingLLM, you could execute a call to the `/export-data` endpoint of the system and then unzip and read that exCVE-2024-0765 · Other software · mintplex-labs · reported by security@huntr.devMedium 6.5
As a default user on a multi-user instance of AnythingLLM, you could execute a call to the `/export-data` endpoint of the system and then unzip and read that export that would enable you do exfiltrate data of the system at that save state. This would require the attacked to be granted explicit access to the system, but they can do this at any role. Additionally, post-download, the data is deleted so no evidence would exist that the exfiltration occured.
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Mar 2, 2024If an attacked was given access to an instance with the admin or manager role there is no backend authentication that would prevent the attacked from creating aCVE-2024-0795 · Other software · mintplex-labs · reported by security@huntr.devHigh 7.2
If an attacked was given access to an instance with the admin or manager role there is no backend authentication that would prevent the attacked from creating a new user with an `admin` role and then be able to use this new account to have elevated privileges on the instance
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Mar 2, 2024In the Linux kernel, the following vulnerability has been resolved: platform/x86: think-lmi: Fix reference leak If a duplicate attribute is found using kset_fCVE-2023-52520 · Computers, phones & browsers · Linux · reported by 416baaa9-dc9f-4396-8d5f-8c081fb06d67Medium 5.5
In the Linux kernel, the following vulnerability has been resolved: platform/x86: think-lmi: Fix reference leak If a duplicate attribute is found using kset_find_obj(), a reference to that attribute is returned which needs to be disposed accordingly using kobject_put(). Move the setting name validation into a separate function to allow for this change without having to duplicate the cleanup code for this setting. As a side note, a very similar bug was fixed in commit 7295a996fdab ("platform/x86: dell-sysman: Fix reference leak"), so it seems that the bug was copied from that driver. Compile-tested only.
- Product
- Linux
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordgit.kernel.orggit.kernel.org
Mar 1, 2024A directory listing vulnerability in Customer Support System v1 allows attackers to list directories and sensitive files within the application without requirinCVE-2023-49545 · Other software · sourcecodester · reported by MITREHigh 7.5
A directory listing vulnerability in Customer Support System v1 allows attackers to list directories and sensitive files within the application without requiring authorization.
- Product
- customer_support_system
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordcwe.mitre.orggithub.com
Mar 1, 2024Previous versions of HP ThinPro (prior to HP ThinPro 8.0 SP 8) could potentially contain security vulnerabilities.CVE-2024-1174 · Other software · HP Inc. · reported by hp-security-alert@hp.comHigh 8.2
Previous versions of HP ThinPro (prior to HP ThinPro 8.0 SP 8) could potentially contain security vulnerabilities. HP has released HP ThinPro 8.0 SP 8, which includes updates to mitigate potential vulnerabilities.
- Product
- HP ThinPro 8.0
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordsupport.hp.comsupport.hp.com
Mar 1, 2024Stupid Simple CMS 1.2.4 is vulnerable to Cross Site Scripting (XSS) within the blog title of the settings.CVE-2024-27558 · Other software · stupid_simple · reported by MITREMedium 6.1
Stupid Simple CMS 1.2.4 is vulnerable to Cross Site Scripting (XSS) within the blog title of the settings.
- Product
- cms
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 28, 2024An issue exists within Piwigo before v.14.2.0 allowing a malicious user to take over the application.CVE-2024-26450 · Other software · Piwigo · reported by MITREMedium 5.4
An issue exists within Piwigo before v.14.2.0 allowing a malicious user to take over the application. This exploit involves chaining a Cross Site Request Forgery vulnerability to issue a Stored Cross Site Scripting payload stored within an Admin user's dashboard, executing remote JavaScript. This can be used to upload a new PHP file under an administrator and directly call that file from the victim's instance to connect back to a malicious listener.
- Product
- Piwigo
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 28, 2024In the Linux kernel, the following vulnerability has been resolved: nvmet-tcp: fix incorrect locking in state_change sk callback We are not changing anything CVE-2021-47041 · Computers, phones & browsers · Linux · reported by 416baaa9-dc9f-4396-8d5f-8c081fb06d67High 7.5
In the Linux kernel, the following vulnerability has been resolved: nvmet-tcp: fix incorrect locking in state_change sk callback We are not changing anything in the TCP connection state so we should not take a write_lock but rather a read lock. This caused a deadlock when running nvmet-tcp and nvme-tcp on the same system, where state_change callbacks on the host and on the controller side have causal relationship and made lockdep report on this with blktests: ================================ WARNING: inconsistent lock state 5.12.0-rc3 #1 Tainted: G I -------------------------------- inconsistent {IN-SOFTIRQ-W} -> {SOFTIRQ-ON-R} usage. nvme/1324 [HC0[0]:SC0[0]:HE1:SE1] takes: ffff888363151000 (clock-AF_INET){++-?}-{2:2}, at: nvme_tcp_state_change+0x21/0x150 [nvme_tcp] {IN-SOFTIRQ-W} state was registered at: __lock_acquire+0x79b/0x18d0 lock_acquire+0x1ca/0x480 _raw_write_lock_bh+0x39/0x80 nvmet_tcp_state_change+0x21/0x170 [nvmet_tcp] tcp_fin+0x2a8/0x780 tcp_data_queue+0xf94/0x1f20 tcp_rcv_established+0x6ba/0x1f00 tcp_v4_do_rcv+0x502/0x760 tcp_v4_rcv+0x257e/0x3430 ip_protocol_deliver_rcu+0x69/0x6a0 ip_local_deliver_finish+0x1e2/0x2f0 ip_local_deliv
- Product
- Linux
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordgit.kernel.orggit.kernel.org
Feb 28, 2024A user who is privileged already `manager` or `admin` can set their profile picture via the frontend API using a relative filepath to then user the PFP GET API CVE-2024-0550 · Other software · mintplex-labs · reported by security@huntr.devMedium 6.5
A user who is privileged already `manager` or `admin` can set their profile picture via the frontend API using a relative filepath to then user the PFP GET API to download any valid files. The attacker would have to have been granted privileged permissions to the system before executing this attack.
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 27, 2024Any user can delete an arbitrary folder (recursively) on a remote server due to bad input sanitization leading to path traversal.CVE-2024-0763 · Other software · mintplex-labs · reported by security@huntr.devHigh 8.1
Any user can delete an arbitrary folder (recursively) on a remote server due to bad input sanitization leading to path traversal. The attacker would need access to the server at some privilege level since this endpoint is protected and requires authorization.
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 27, 2024Enable exports of the database and associated exported information of the system via the default user role.CVE-2024-0551 · Other software · mintplex-labs · reported by security@huntr.devHigh 7.1
Enable exports of the database and associated exported information of the system via the default user role. The attacked would have to have been granted access to the system prior to the attack. It is worth noting that the deterministic nature of the export name is lower risk as the UI for exporting would start the download at the same time, which once downloaded - deletes the export from the system. The endpoint for exporting should simply be patched to a higher privilege level.
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 27, 2024Should an instance of AnythingLLM be hosted on an internal network and the attacked be explicitly granted a permission level of manager or admin, they could linCVE-2024-0759 · Other software · mintplex-labs · reported by security@huntr.devHigh 7.5
Should an instance of AnythingLLM be hosted on an internal network and the attacked be explicitly granted a permission level of manager or admin, they could link-scrape internally resolving IPs of other services that are on the same network as AnythingLLM. This would require the attacker also be able to guess these internal IPs as `/*` ranging is not possible, but could be brute forced. There is a duty of care that other services on the same network would not be fully open and accessible via a simple CuRL with zero authentication as it is not possible to set headers or access via the link collector.
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 26, 2024A privilege escalation vulnerability exists in mintplex-labs/anything-llm, allowing users with 'default' role to delete documents uploaded by 'admin'.CVE-2024-0798 · Other software · mintplex-labs · reported by security@huntr.devMedium 6.5
A privilege escalation vulnerability exists in mintplex-labs/anything-llm, allowing users with 'default' role to delete documents uploaded by 'admin'. Despite the intended restriction that prevents 'default' role users from deleting admin-uploaded documents, an attacker can exploit this vulnerability by sending a crafted DELETE request to the /api/system/remove-document endpoint. This vulnerability is due to improper access control checks, enabling unauthorized document deletion and potentially leading to loss of data integrity.
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 26, 2024The inclusion of the web scraper for AnythingLLM means that any user with the proper authorization level (manager, admin, and when in single user) could put in CVE-2024-0455 · Other software · mintplex-labs · reported by security@huntr.devHigh 7.5
The inclusion of the web scraper for AnythingLLM means that any user with the proper authorization level (manager, admin, and when in single user) could put in the URL ``` http://169.254.169.254/latest/meta-data/identity-credentials/ec2/security-credentials/ec2-instance ``` which is a special IP and URL that resolves only when the request comes from within an EC2 instance. This would allow the user to see the connection/secret credentials for their specific instance and be able to manage it regardless of who deployed it. The user would have to have pre-existing knowledge of the hosting infra which the target instance is deployed on, but if sent - would resolve if on EC2 and the proper `iptable` or firewall rule is not configured for their setup.
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 26, 2024Attacker, with permission to submit a link or submits a link via POST to be collected that is using the file:// protocol can then introspect host files and othCVE-2024-0440 · Other software · mintplex-labs · reported by security@huntr.devMedium 6.5
Attacker, with permission to submit a link or submits a link via POST to be collected that is using the file:// protocol can then introspect host files and other relatively stored files.
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 26, 2024As a manager, you should not be able to modify a series of settings.CVE-2024-0439 · Other software · mintplex-labs · reported by security@huntr.devHigh 8.8
As a manager, you should not be able to modify a series of settings. In the UI this is indeed hidden as a convenience for the role since most managers would not be savvy enough to modify these settings. They can use their token to still modify those settings though through a standard HTTP request While this is not a critical vulnerability, it does indeed need to be patched to enforce the expected permission level.
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 26, 2024Theoretically, it would be possible for an attacker to brute-force the password for an instance in single-user password protection mode via a timing attack giveCVE-2024-0436 · Other software · mintplex-labs · reported by security@huntr.devMedium 5.9
Theoretically, it would be possible for an attacker to brute-force the password for an instance in single-user password protection mode via a timing attack given the linear nature of the `!==` used for comparison. The risk is minified by the additional overhead of the request, which varies in a non-constant nature making the attack less reliable to execute
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 26, 2024User can send a chat that contains an XSS opportunity that will then run when the chat is sent and on subsequent page loads.CVE-2024-0435 · Other software · mintplex-labs · reported by security@huntr.devMedium 5.4
User can send a chat that contains an XSS opportunity that will then run when the chat is sent and on subsequent page loads. Given the minimum requirement for a user to send a chat is to be given access to a workspace via an admin the risk is low. Additionally, the location in which the XSS renders is only limited to the user who submits the XSS. Ultimately, this attack is limited to the user attacking themselves. There is no anonymous chat submission unless the user does not take the minimum steps required to protect their instance.
- Product
- mintplex-labs/anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 22, 2024### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`ChoCVE-2024-26152 · Other software · HumanSignal · reported by GitHubMedium 4.7
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 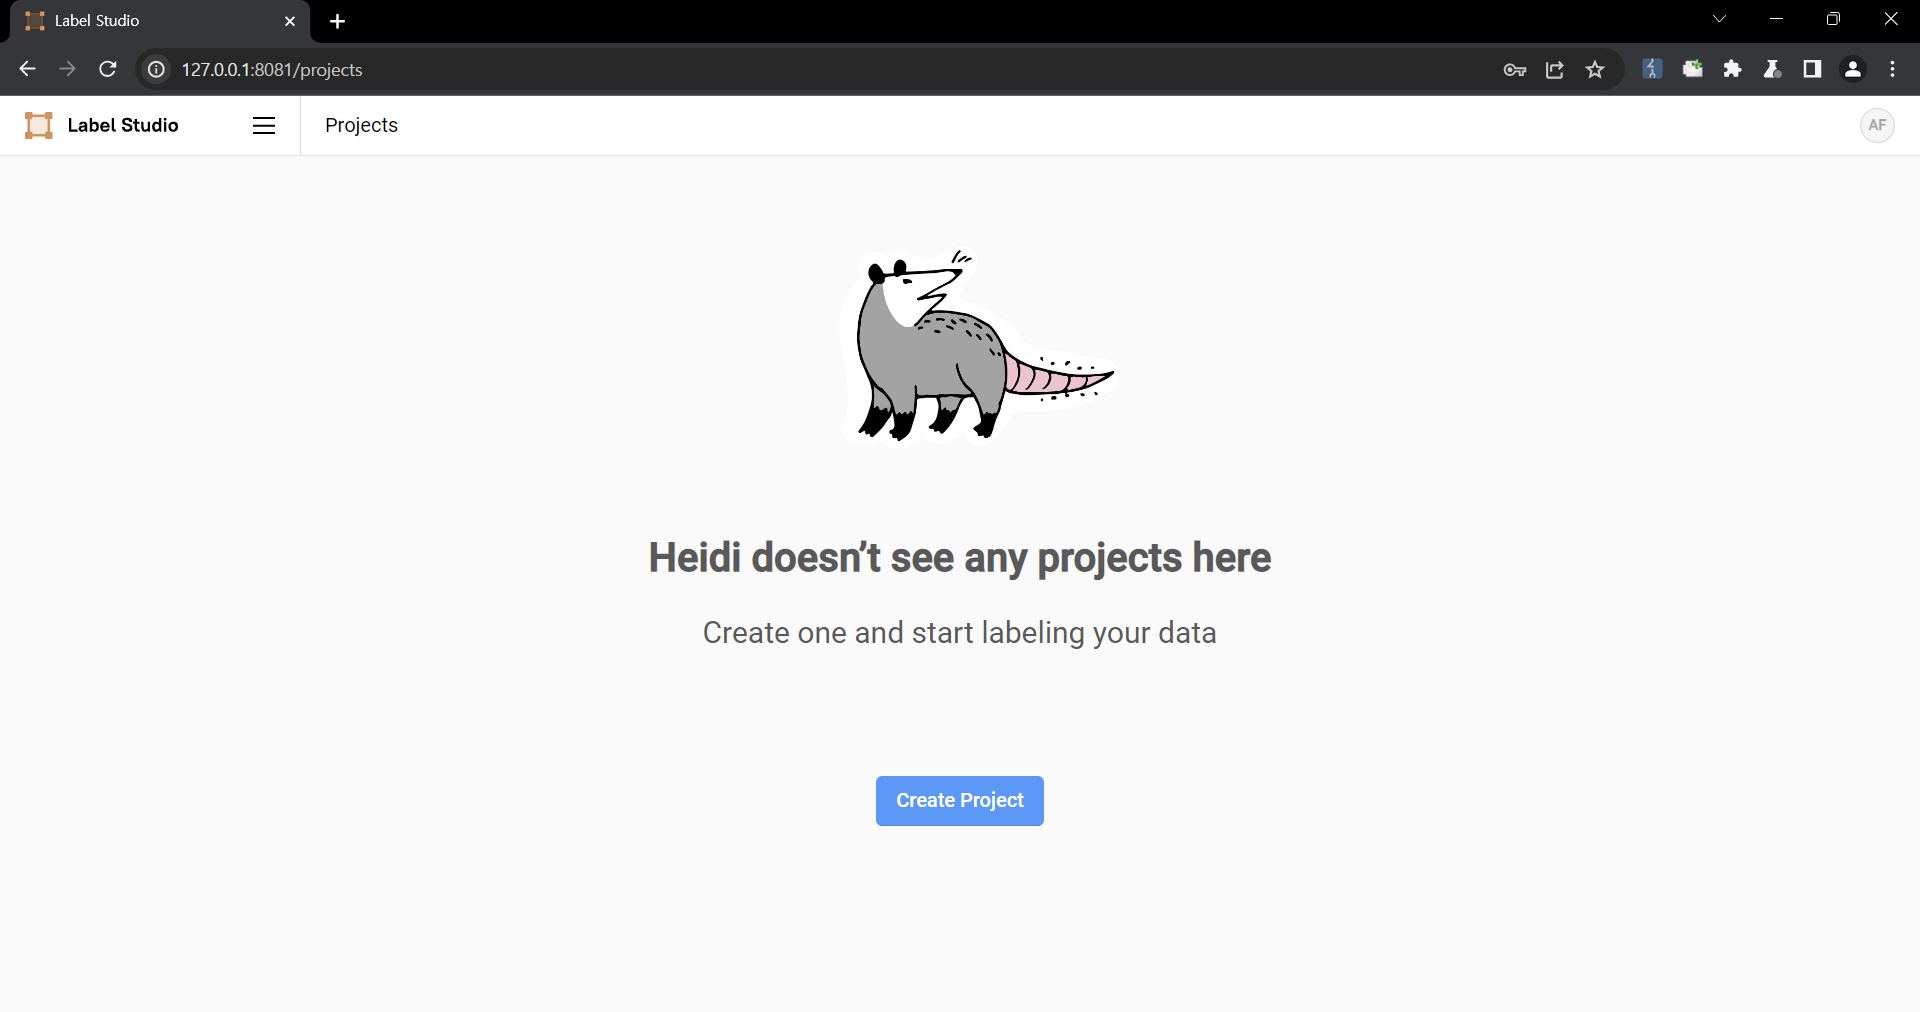 2. Upload a file containing the payload using the "Upload Files" function. 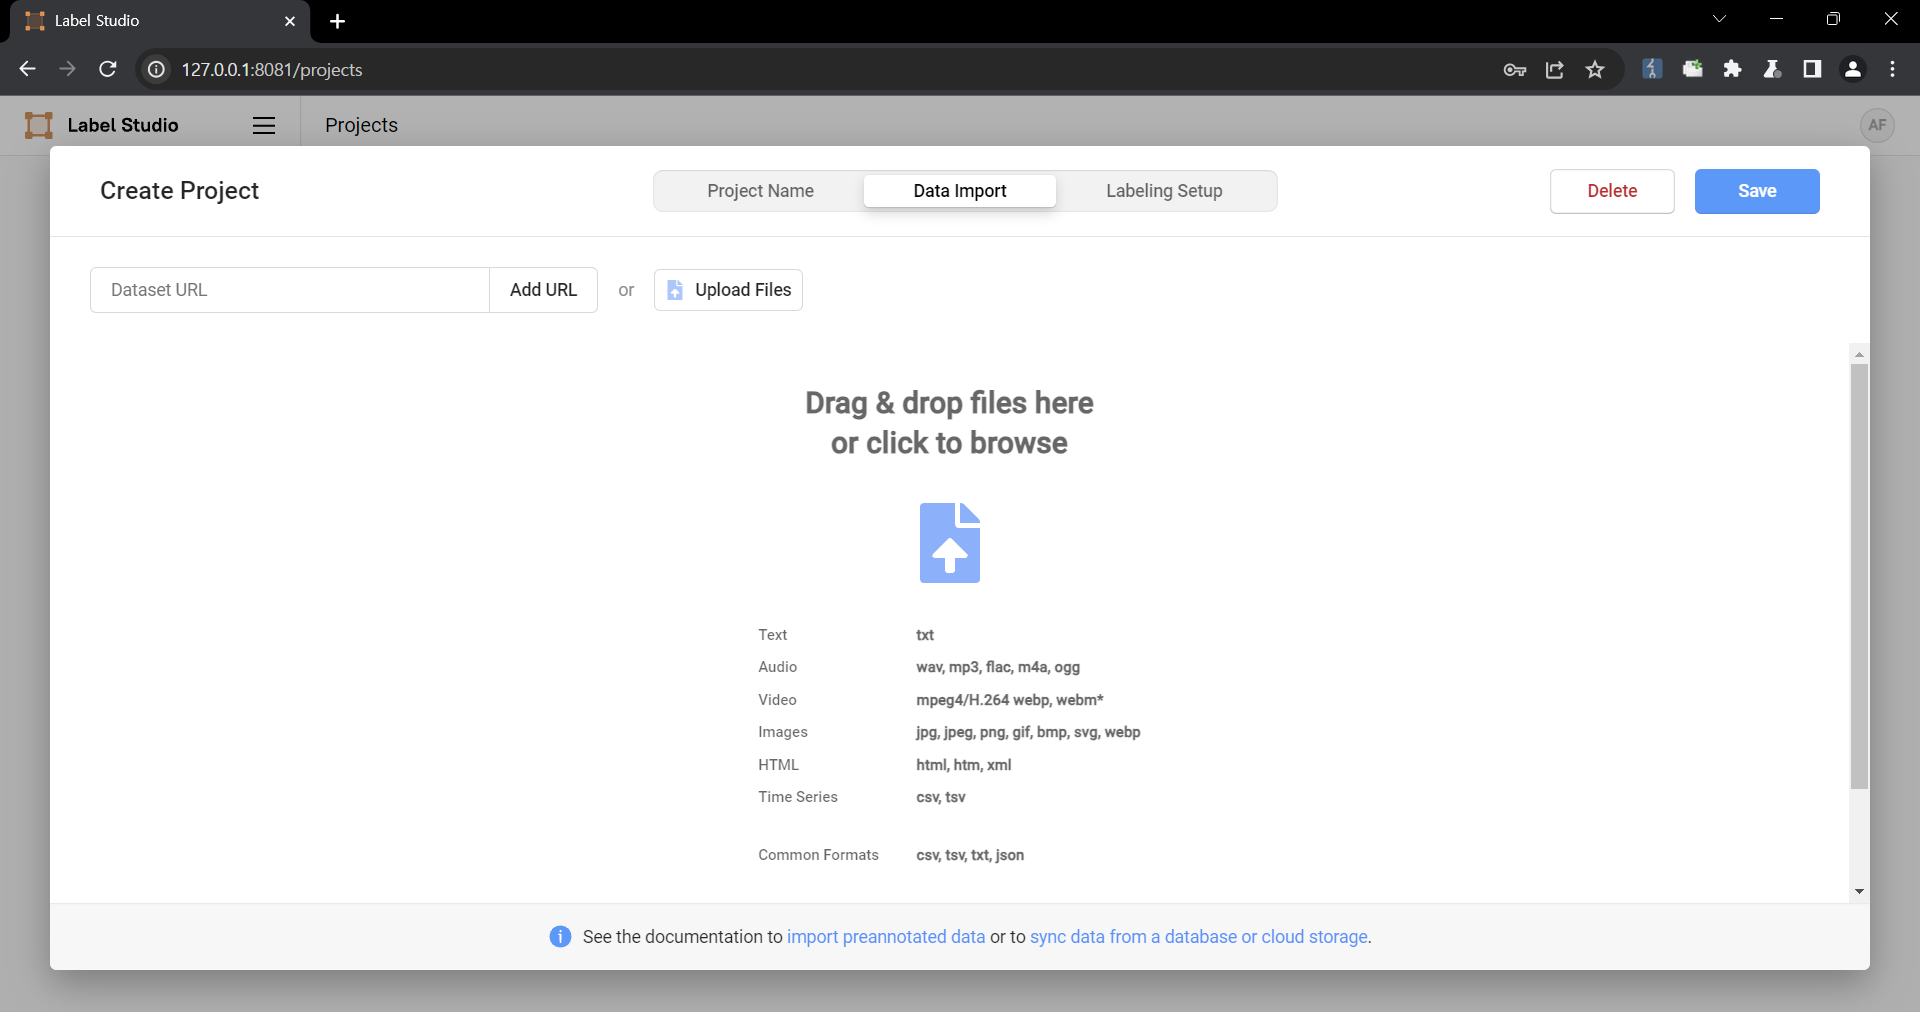 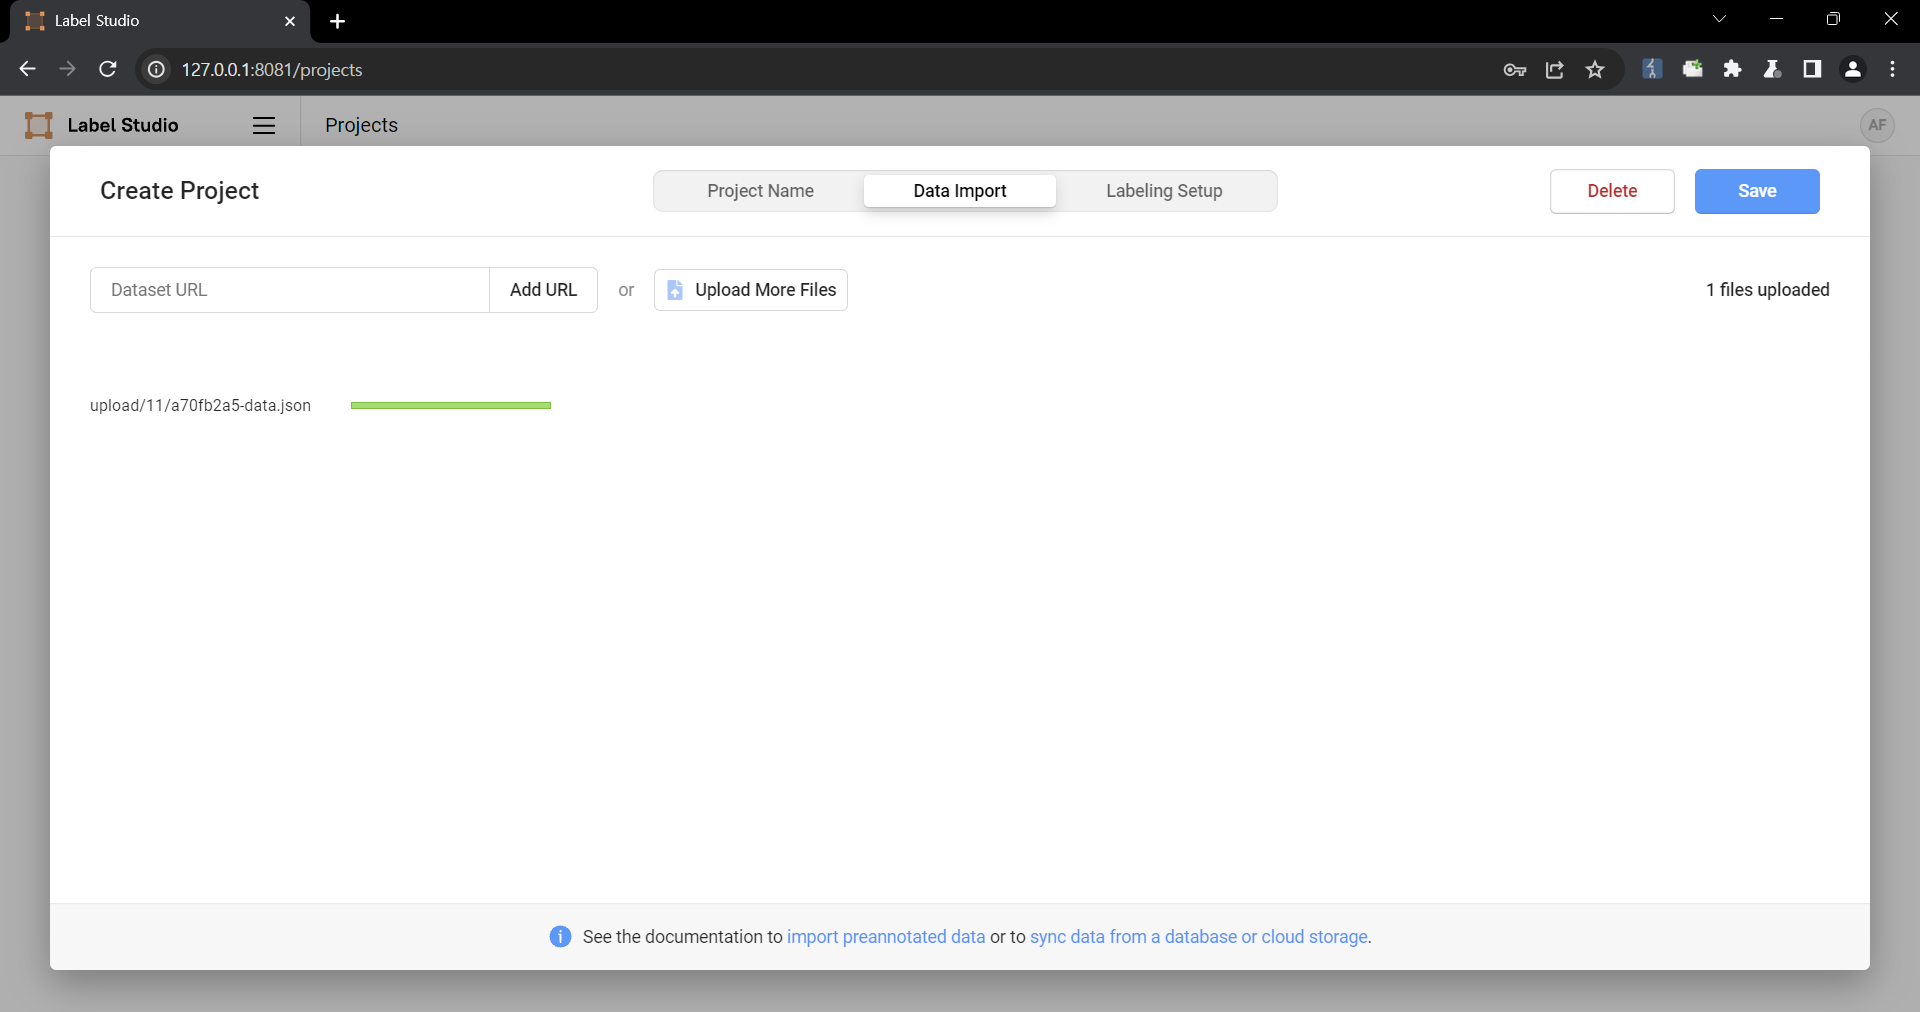 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 16, 2024ThinkSystem SR670V2 servers manufactured from approximately June 2021 to July 2023 were left in Manufacturing Mode which could allow an attacker with privilegCVE-2024-23591 · Other software · Lenovo · reported by psirt@lenovo.comLow 2
ThinkSystem SR670V2 servers manufactured from approximately June 2021 to July 2023 were left in Manufacturing Mode which could allow an attacker with privileged logical access to the host or physical access to server internals to modify or disable Intel Boot Guard firmware integrity, SPS security, and other SPS configuration setting. The server’s NIST SP 800-193-compliant Platform Firmware Resiliency (PFR) security subsystem significantly mitigates this issue.
- Product
- ThinkSystem SR670 V2
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordsupport.lenovo.comhttps
Feb 16, 2024In Hazelcast Platform through 5.3.4, a security issue exists within the SQL mapping for the CSV File Source connector.CVE-2023-45860 · Other software · Hazelcast · reported by MITREMedium 6.5
In Hazelcast Platform through 5.3.4, a security issue exists within the SQL mapping for the CSV File Source connector. This issue arises from inadequate permission checking, which could enable unauthorized clients to access data from files stored on a member's filesystem.
- Product
- Hazelcast
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 15, 2024Use of Hard-coded Credentials vulnerability in Utarit Information Technologies SoliPay Mobile App allows Read Sensitive Strings Within an Executable.CVE-2023-6255 · Other software · Utarit Information Technologies · reported by iletisim@usom.gov.trHigh 7.5
Use of Hard-coded Credentials vulnerability in Utarit Information Technologies SoliPay Mobile App allows Read Sensitive Strings Within an Executable. This issue affects SoliPay Mobile App: before 5.0.8.
- Product
- SoliPay Mobile App
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordsiberguvenlik.gov.trusom.gov.tr
Feb 14, 2024Command Injection vulnerability discovered in 4ipnet EAP-767 device v3.42.00 within the web interface of the device allows attackers with valid credentials to iCVE-2024-24301 · Other software · 4ipnet · reported by MITREHigh 8.8
Command Injection vulnerability discovered in 4ipnet EAP-767 device v3.42.00 within the web interface of the device allows attackers with valid credentials to inject arbitrary shell commands to be executed by the device with root privileges.
- Product
- eap-767
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 12, 2024 Dell Unity, versions prior to 5.4, contains an OS Command Injection Vulnerability within its svc_cbr utility.CVE-2024-22223 · Other software · Dell · reported by security_alert@emc.comHigh 7.8
Dell Unity, versions prior to 5.4, contains an OS Command Injection Vulnerability within its svc_cbr utility. An authenticated malicious user with local access could potentially exploit this vulnerability, leading to the execution of arbitrary OS commands on the application's underlying OS, with the privileges of the vulnerable application.
- Product
- Unity
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 12, 2024 Dell Unity, versions prior to 5.4, contains an OS Command Injection Vulnerability within its svc_udoctor utility.CVE-2024-22222 · Other software · Dell · reported by security_alert@emc.comHigh 7.8
Dell Unity, versions prior to 5.4, contains an OS Command Injection Vulnerability within its svc_udoctor utility. An authenticated malicious user with local access could potentially exploit this vulnerability, leading to the execution of arbitrary OS commands on the application's underlying OS, with the privileges of the vulnerable application.
- Product
- Unity
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 11, 2024qanything_kernel/connector/database/mysql/mysql_client.py in qanything.ai QAnything before 1.2.0 allows SQL Injection.CVE-2024-25722 · Other software · Qanything · reported by MITRECritical 9.8
qanything_kernel/connector/database/mysql/mysql_client.py in qanything.ai QAnything before 1.2.0 allows SQL Injection.
- Product
- Qanything
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 6, 2024In JetBrains TeamCity before 2023.11.3 path traversal allowed reading data within JAR archivesCVE-2024-24942 · Other software · JetBrains · reported by cve@jetbrains.comMedium 5.3
In JetBrains TeamCity before 2023.11.3 path traversal allowed reading data within JAR archives
- Product
- TeamCity
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordjetbrains.comjetbrains.com
Feb 5, 2024Allegro AI’s open-source version of ClearML stores passwords in plaintext within the MongoDB instance, resulting in a compromised server leaking all user emailsCVE-2024-24595 · Other software · Allegro.AI · reported by 6f8de1f0-f67e-45a6-b68f-98777fdb759cMedium 6
Allegro AI’s open-source version of ClearML stores passwords in plaintext within the MongoDB instance, resulting in a compromised server leaking all user emails and passwords.
- Product
- ClearML
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordhiddenlayer.comhiddenlayer.com
Feb 1, 2024 MachineSense FeverWarn devices are configured as Wi-Fi hosts in a way that attackers within range could connect to the device's web services and comproCVE-2023-47867 · Other software · MachineSense · reported by ics-cert@hq.dhs.govHigh 8.8
MachineSense FeverWarn devices are configured as Wi-Fi hosts in a way that attackers within range could connect to the device's web services and compromise the device.
- Product
- FeverWarn
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmachinesense.comcisa.gov
Jan 26, 2024A vulnerability with the access control list (ACL) management within a stacked switch configuration of Cisco Business 250 Series Smart Switches and Business 350CVE-2024-20263 · Network & remote access · Cisco · reported by psirt@cisco.comMedium 5.8
A vulnerability with the access control list (ACL) management within a stacked switch configuration of Cisco Business 250 Series Smart Switches and Business 350 Series Managed Switches could allow an unauthenticated, remote attacker to bypass protection offered by a configured ACL on an affected device. This vulnerability is due to incorrect processing of ACLs on a stacked configuration when either the primary or backup switches experience a full stack reload or power cycle. An attacker could exploit this vulnerability by sending crafted traffic through an affected device. A successful exploit could allow the attacker to bypass configured ACLs, causing traffic to be dropped or forwarded in an unexpected manner. The attacker does not have control over the conditions that result in the device being in the vulnerable state. Note: In the vulnerable state, the ACL would be correctly applied on the primary devices but could be incorrectly applied to the backup devices.
- Product
- Cisco Small Business Smart and Managed Switches
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordsec.cloudapps.cisco.comsec.cloudapps.cisco.com
Jan 23, 2024 Lantronix XPort sends weakly encoded credentials within web request headers.CVE-2023-7237 · Other software · Lantronix · reported by ics-cert@hq.dhs.govMedium 5.7
Lantronix XPort sends weakly encoded credentials within web request headers.
- Product
- XPort
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 18, 2024AnythingLLM is an application that turns any document, resource, or piece of content into context that any LLM can use as references during chatting.CVE-2024-22422 · Other software · Mintplex-Labs · reported by GitHubHigh 7.5
AnythingLLM is an application that turns any document, resource, or piece of content into context that any LLM can use as references during chatting. In versions prior to commit `08d33cfd8` an unauthenticated API route (file export) can allow attacker to crash the server resulting in a denial of service attack. The “data-export” endpoint is used to export files using the filename parameter as user input. The endpoint takes the user input, filters it to avoid directory traversal attacks, fetches the file from the server, and afterwards deletes it. An attacker can trick the input filter mechanism to point to the current directory, and while attempting to delete it the server will crash as there is no error-handling wrapper around it. Moreover, the endpoint is public and does not require any form of authentication, resulting in an unauthenticated Denial of Service issue, which crashes the instance using a single HTTP packet. This issue has been addressed in commit `08d33cfd8`. Users are advised to upgrade. There are no known workarounds for this vulnerability.
- Product
- anything-llm
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 18, 2024Nextcloud files Zip app is a tool to create zip archives from one or multiple files from within Nextcloud.CVE-2024-22404 · Other software · nextcloud · reported by GitHubMedium 4.1
Nextcloud files Zip app is a tool to create zip archives from one or multiple files from within Nextcloud. In affected versions users can download "view-only" files by zipping the complete folder. It is recommended that the Files ZIP app is upgraded to 1.2.1, 1.4.1, or 1.5.0. Users unable to upgrade should disable the file zip app.
- Product
- security-advisories
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 16, 2024In D-LINK Go-RT-AC750 v101b03, the sprintf function in the sub_40E700 function within the cgibin is susceptible to stack overflow.CVE-2024-22916 · Other software · dlink · reported by MITRECritical 9.8
In D-LINK Go-RT-AC750 v101b03, the sprintf function in the sub_40E700 function within the cgibin is susceptible to stack overflow.
- Product
- go-rt-ac750_firmware
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordkee02p.github.iodlink.com
Jan 16, 2024Improper Restriction of Operations within the Bounds of a Memory Buffer vulnerability in HYPR Workforce Access on Windows allows Overflow Buffers.This issue affCVE-2023-6334 · Other software · HYPR · reported by security@hypr.comMedium 5.3
Improper Restriction of Operations within the Bounds of a Memory Buffer vulnerability in HYPR Workforce Access on Windows allows Overflow Buffers.This issue affects Workforce Access: before 8.7.
- Product
- Workforce Access
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 16, 2024Print Invoice & Delivery Notes for WooCommerce: Is vulnerable to reflected XSS by echoing a GET value in an admin note within the WooCommerce orders pageCVE-2023-0479 · WordPress plugins & themes · reported by WPScanMedium 6.1
The Print Invoice & Delivery Notes for WooCommerce WordPress plugin before 4.7.2 is vulnerable to reflected XSS by echoing a GET value in an admin note within the WooCommerce orders page. This means that this vulnerability can be exploited for users with the edit_others_shop_orders capability. WooCommerce must be installed and active. This vulnerability is caused by a urldecode() after cleanup with esc_url_raw(), allowing double encoding.
- Product
- Print Invoice & Delivery Notes for WooCommerce
- Fixed in
- 4.7.2
- What to do
- Update Print Invoice & Delivery Notes for WooCommerce to 4.7.2 or newer.
Jan 16, 2024Slide Anything: Does not properly sanitize or escape the slide title before outputting it in the admin pagesCVE-2022-2413 · WordPress plugins & themes · reported by WPScanMedium 5.4
The Slide Anything WordPress plugin before 2.3.47 does not properly sanitize or escape the slide title before outputting it in the admin pages, allowing a logged in user with roles as low as Author to inject a javascript payload into the slide title even when the unfiltered_html capability is disabled.
- Product
- Slide Anything
- Fixed in
- 2.3.47
- What to do
- Update Slide Anything to 2.3.47 or newer.
Jan 14, 2024NetVision Information airPASS has a path traversal vulnerability within its parameter in a specific URL.CVE-2023-48383 · Other software · NetVision Information · reported by twcert@cert.org.twHigh 7.5
NetVision Information airPASS has a path traversal vulnerability within its parameter in a specific URL. An unauthenticated remote attacker can exploit this vulnerability to bypass authentication and download arbitrary system files.
- Product
- airPASS
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordtwcert.org.twtwcert.org.tw
Jan 12, 2024QStar Archive Solutions Release RELEASE_3-0 Build 7 Patch 0 was discovered to contain a DOM Based reflected XSS vulnerability within the component qnme-ajax?metCVE-2023-51064 · Other software · Qstar · reported by MITREMedium 6.1
QStar Archive Solutions Release RELEASE_3-0 Build 7 Patch 0 was discovered to contain a DOM Based reflected XSS vulnerability within the component qnme-ajax?method=tree_table.
- Product
- Archive Storage Manager
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 12, 2024QStar Archive Solutions Release RELEASE_3-0 Build 7 Patch 0 was discovered to contain a DOM Based Reflected Cross Site Scripting (XSS) vulnerability within the CVE-2023-51063 · Other software · Qstar · reported by MITREHigh 8.8
QStar Archive Solutions Release RELEASE_3-0 Build 7 Patch 0 was discovered to contain a DOM Based Reflected Cross Site Scripting (XSS) vulnerability within the component qnme-ajax?method=tree_level.
- Product
- Archive Storage Manager
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 10, 2024pimcore/customer-data-framework is the Customer Management Framework for management of customer data within Pimcore.CVE-2024-21667 · Other software · pimcore · reported by GitHubMedium 6.5
pimcore/customer-data-framework is the Customer Management Framework for management of customer data within Pimcore. An authenticated and unauthorized user can access the GDPR data extraction feature and query over the information returned, leading to customer data exposure. Permissions are not enforced when reaching the `/admin/customermanagementframework/gdpr-data/search-data-objects` endpoint allowing an authenticated user without the permissions to access the endpoint and query the data available there. An unauthorized user can access PII data from customers. This vulnerability has been patched in version 4.0.6.
- Product
- customer-data-framework
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Where this comes from: the exploited list is CISA’s Known Exploited Vulnerabilities catalog. Everything else is the whole National Vulnerability Database, where each record is published by the team that found the bug (Wordfence, Patchstack, WPScan, the vendors themselves and others); we show who. Exploit odds are FIRST’s EPSS, updated daily. Titles and categories are ours, so check the linked record before acting on a detail. For a write-up of the big ones, see our advisories. Every vendor, and every WordPress plugin and theme with a recorded flaw, also has its own page. All of it is free to reuse as JSON, CSV or RSS.
Weekly security brief
The flaws that hit local websites, every Friday.
One short email: what got exploited this week, which WordPress plugins broke, and what to check. Unsubscribe in one click.
Tell us what you're building.
A website, your marketing, a security check, an app, or the thing you've been running out of a spreadsheet for three years. A few lines is plenty.
Not ready to talk yet? Run the free website check and see what Google sees.