Vulnerability database
Every flaw the U.S. government’s cybersecurity agency (CISA) has confirmed attackers are using, plus the new WordPress plugin and theme bugs published each day, sorted by what they mean for a small business. We refresh it twice a day. If you see something your website or office runs, tell us.
1,520 results · page 13 of 31
Jul 13, 2024Support SVG: Does not sanitize SVG file contentsCVE-2024-4272 · WordPress plugins & themes · reported by WPScanMedium 6.1
The Support SVG WordPress plugin before 1.1.0 does not sanitize SVG file contents, which enables users with at least the author role to SVG with malicious JavaScript to conduct Stored XSS attacks.
- Product
- Support SVG
- Fixed in
- 1.1.0
- What to do
- Update Support SVG to 1.1.0 or newer.
Jul 13, 2024SVG Block: Does not sanitize SVG file contentsCVE-2024-4269 · WordPress plugins & themes · reported by WPScanMedium 6.1
The SVG Block WordPress plugin before 1.1.20 does not sanitize SVG file contents, which enables users with at least the author role to SVG with malicious JavaScript to conduct Stored XSS attacks.
- Product
- SVG Block
- Fixed in
- 1.1.20
- What to do
- Update SVG Block to 1.1.20 or newer.
Jul 3, 2024Mattermost versions 9.5.x <= 9.5.5 and 9.8.0 fail to properly sanitize the recipients of a webhook event which allows an attacker monitoring webhook events to rCVE-2024-39807 · Other software · Mattermost · reported by responsibledisclosure@mattermost.comLow 3.1
Mattermost versions 9.5.x <= 9.5.5 and 9.8.0 fail to properly sanitize the recipients of a webhook event which allows an attacker monitoring webhook events to retrieve the channel IDs of archived or restored channels.
- Product
- Mattermost
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmattermost.commattermost.com
Jul 3, 2024Mattermost versions 9.5.x <= 9.5.5 and 9.8.0 fail to sanitize the RemoteClusterFrame payloads before audit logging them which allows a high privileged attacker CVE-2024-39353 · Other software · Mattermost · reported by responsibledisclosure@mattermost.comLow 2.7
Mattermost versions 9.5.x <= 9.5.5 and 9.8.0 fail to sanitize the RemoteClusterFrame payloads before audit logging them which allows a high privileged attacker with access to the audit logs to read message contents.
- Product
- Mattermost
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmattermost.commattermost.com
Jun 24, 2024go-retryablehttp prior to 0.7.7 did not sanitize urls when writing them to its log file.CVE-2024-6104 · Other software · HashiCorp · reported by security@hashicorp.comMedium 6
go-retryablehttp prior to 0.7.7 did not sanitize urls when writing them to its log file. This could lead to go-retryablehttp writing sensitive HTTP basic auth credentials to its log file. This vulnerability, CVE-2024-6104, was fixed in go-retryablehttp 0.7.7.
- Product
- Shared library
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddiscuss.hashicorp.comdiscuss.hashicorp.com
Jun 20, 2024HTML5 Video Player: Does not sanitize and escape a parameter from a REST route before using it in a SQL statementCVE-2024-5522 · WordPress plugins & themes · reported by WPScanMedium 6.5
The HTML5 Video Player WordPress plugin before 2.5.27 does not sanitize and escape a parameter from a REST route before using it in a SQL statement, allowing unauthenticated users to perform SQL injection attacks
- Product
- HTML5 Video Player
- Fixed in
- 2.5.27
- What to do
- Update HTML5 Video Player to 2.5.27 or newer.
Jun 14, 2024SVGator: Does not sanitize SVG file contentsCVE-2024-4271 · WordPress plugins & themes · reported by WPScanMedium 4.6
The SVGator WordPress plugin through 1.2.6 does not sanitize SVG file contents, which enables users with at least the author role to SVG with malicious JavaScript to conduct Stored XSS attacks.
- Product
- SVGator
- Affected
- up to 1.2.6
- What to do
- Affects up to 1.2.6. Update SVGator to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Jun 14, 2024SVGMagic: Does not sanitize SVG file contentsCVE-2024-4270 · WordPress plugins & themes · reported by WPScanMedium 5.4
The SVGMagic WordPress plugin through 1.1 does not sanitize SVG file contents, which enables users with at least the author role to SVG with malicious JavaScript to conduct Stored XSS attacks.
- Product
- SVGMagic
- Affected
- up to 1.1
- What to do
- Affects up to 1.1. Update SVGMagic to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Jun 13, 2024Search & Replace: Does not sanitize and escape a parameter before using it in a SQL statementCVE-2024-4145 · WordPress plugins & themes · reported by WPScanHigh 7.2
The Search & Replace WordPress plugin before 3.2.2 does not sanitize and escape a parameter before using it in a SQL statement, allowing admins to perform SQL injection attacks (such as within a multi-site network).
- Product
- Search & Replace
- Fixed in
- 3.2.2
- What to do
- Update Search & Replace to 3.2.2 or newer.
Jun 6, 2024A path traversal vulnerability exists in the parisneo/lollms application, specifically within the `sanitize_path_from_endpoint` and `sanitize_path` functions inCVE-2024-3429 · Other software · parisneo · reported by security@huntr.devCritical 9.8
A path traversal vulnerability exists in the parisneo/lollms application, specifically within the `sanitize_path_from_endpoint` and `sanitize_path` functions in `lollms_core\lollms\security.py`. This vulnerability allows for arbitrary file reading when the application is running on Windows. The issue arises due to insufficient sanitization of user-supplied input, enabling attackers to bypass the path traversal protection mechanisms by crafting malicious input. Successful exploitation could lead to unauthorized access to sensitive files, information disclosure, and potentially a denial of service (DoS) condition by including numerous large or resource-intensive files. This vulnerability affects the latest version prior to 9.6.
- Product
- parisneo/lollms
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jun 4, 2024wp-eMember: Does not sanitize and escape the "fieldId" parameter before outputting it back in the pageCVE-2024-4749 · WordPress plugins & themes · reported by WPScanHigh 8.3
The wp-eMember WordPress plugin before 10.3.9 does not sanitize and escape the "fieldId" parameter before outputting it back in the page, leading to a Reflected Cross-Site Scripting.
- Product
- wp-eMember
- Fixed in
- 10.3.9
- What to do
- Update wp-eMember to 10.3.9 or newer.
Jun 4, 2024Events Calendar: Does not properly sanitize user-submitted contentCVE-2024-4180 · WordPress plugins & themes · reported by WPScanCritical 9.1
The Events Calendar WordPress plugin before 6.4.0.1 does not properly sanitize user-submitted content when rendering some views via AJAX.
- Product
- Events Calendar
- Fixed in
- 6.4.0.1
- What to do
- Update Events Calendar to 6.4.0.1 or newer.
May 27, 2024KKProgressbar2 Free: Does not sanitize and escape a parameter before using it in a SQL statementCVE-2024-4533 · WordPress plugins & themes · reported by WPScanMedium 6.5
The KKProgressbar2 Free WordPress plugin through 1.1.4.2 does not sanitize and escape a parameter before using it in a SQL statement, allowing admin users to perform SQL injection attacks
- Product
- KKProgressbar2 Free
- Affected
- up to 1.1.4.2
- What to do
- Affects up to 1.1.4.2. Update KKProgressbar2 Free to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
May 24, 2024Mocodo Mocodo Online 4.2.6 and below does not properly sanitize the sql_case input field in /web/generate.php, allowing remote attackers to execute arbitrary coCVE-2024-35374 · Other software · mocodo · reported by MITRECritical 9.8
Mocodo Mocodo Online 4.2.6 and below does not properly sanitize the sql_case input field in /web/generate.php, allowing remote attackers to execute arbitrary commands and potentially command injection, leading to remote code execution (RCE) under certain conditions.
- Product
- mocodo_online
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordchocapikk.comgithub.com
May 14, 2024The WPS Office (aka cn.wps.moffice_eng) application before 17.0.0 for Android fails to properly sanitize file names before processing them through external applCVE-2024-35205 · Other software · kingsoft · reported by MITREHigh 7.8
The WPS Office (aka cn.wps.moffice_eng) application before 17.0.0 for Android fails to properly sanitize file names before processing them through external application interactions, leading to a form of path traversal. This potentially enables any application to dispatch a crafted library file, aiming to overwrite an existing native library utilized by WPS Office. Successful exploitation could result in the execution of arbitrary commands under the guise of WPS Office's application ID.
- Product
- wps_office
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmicrosoft.commicrosoft.com
May 6, 2024html-sanitizer is an allowlist-based HTML cleaner.CVE-2024-34078 · Other software · matthiask · reported by GitHubMedium 6.1
html-sanitizer is an allowlist-based HTML cleaner. If using `keep_typographic_whitespace=False` (which is the default), the sanitizer normalizes unicode to the NFKC form at the end. Some unicode characters normalize to chevrons; this allows specially crafted HTML to escape sanitization. The problem has been fixed in 2.4.2.
- Product
- html-sanitizer
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Apr 26, 2024ENL Newsletter: Does not sanitize and escape a parameter before using it in a SQL statementCVE-2024-3060 · WordPress plugins & themes · reported by WPScanMedium 4.5
The ENL Newsletter WordPress plugin through 1.0.1 does not sanitize and escape a parameter before using it in a SQL statement, allowing admin+ to perform SQL injection attacks
- Product
- ENL Newsletter
- Affected
- up to 1.0.1
- What to do
- Affects up to 1.0.1. Update ENL Newsletter to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Apr 17, 2024Salon booking system: Does not properly sanitize and escape the 'Mobile Phone' field and 'sms_prefix' parameterCVE-2024-2102 · WordPress plugins & themes · reported by WPScanMedium 4.7
The Salon booking system WordPress plugin before 9.6.3 does not properly sanitize and escape the 'Mobile Phone' field and 'sms_prefix' parameter when booking an appointment, allowing customers to conduct Stored Cross-Site Scripting attacks. The payload gets triggered when an admin visits the 'Bookings' page and the malicious script is executed in the admin context.
- Product
- Salon booking system
- Fixed in
- 9.6.3
- What to do
- Update Salon booking system to 9.6.3 or newer.
Apr 17, 2024Salon booking system: Does not properly sanitize and escape the 'Mobile Phone' fieldCVE-2024-2101 · WordPress plugins & themes · reported by WPScanMedium 5.7
The Salon booking system WordPress plugin before 9.6.3 does not properly sanitize and escape the 'Mobile Phone' field when booking an appointment, allowing customers to conduct Stored Cross-Site Scripting attacks. The payload gets triggered when an admin visits the 'Customers' page and the malicious script is executed in the admin context.
- Product
- Salon booking system
- Fixed in
- 9.6.3
- What to do
- Update Salon booking system to 9.6.3 or newer.
Apr 14, 2024The Web interface of Evolution Controller Versions 2.04.560.31.03.2024 and below does not proper sanitize user input, allowing for an unauthenticated attacker CVE-2024-29838 · Other software · CS Technologies Australia · reported by 430a6cef-dc26-47e3-9fa8-52fb7f19644eHigh 7.5
The Web interface of Evolution Controller Versions 2.04.560.31.03.2024 and below does not proper sanitize user input, allowing for an unauthenticated attacker to crash the controller software
- Product
- Evolution Controller
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddirectcyber.com.audirectcyber.com.au
Apr 2, 2024In the Linux kernel, the following vulnerability has been resolved: netfilter: nft_ct: sanitize layer 3 and 4 protocol number in custom expectations - DisalloCVE-2024-26673 · Computers, phones & browsers · Linux · reported by 416baaa9-dc9f-4396-8d5f-8c081fb06d67High 7.1
In the Linux kernel, the following vulnerability has been resolved: netfilter: nft_ct: sanitize layer 3 and 4 protocol number in custom expectations - Disallow families other than NFPROTO_{IPV4,IPV6,INET}. - Disallow layer 4 protocol with no ports, since destination port is a mandatory attribute for this object.
- Product
- Linux
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordgit.kernel.orggit.kernel.org
Apr 1, 2024Memory corruption in HLOS while running kernel address sanitizers (syzkaller) on tmecom with DEBUG_FS enabled.CVE-2023-43515 · Computers, phones & browsers · Qualcomm, Inc. · reported by product-security@qualcomm.comMedium 6.6
Memory corruption in HLOS while running kernel address sanitizers (syzkaller) on tmecom with DEBUG_FS enabled.
- Product
- Snapdragon
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddocs.qualcomm.comdocs.qualcomm.com
Mar 27, 2024Lektor before 3.3.11 does not sanitize DB path traversal.CVE-2024-28335 · Other software · lektor · reported by MITRECritical 9.1
Lektor before 3.3.11 does not sanitize DB path traversal. Thus, shell commands might be executed via a file that is added to the templates directory, if the victim's web browser accesses an untrusted website that uses JavaScript to send requests to localhost port 5000, and the web browser is running on the same machine as the "lektor server" command.
- Product
- lektor
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbrave.comcxsecurity.com
Mar 20, 2024System Dashboard: Does not sanitize and escape some parametersCVE-2023-7246 · WordPress plugins & themes · reported by WPScanMedium 5.4
The System Dashboard WordPress plugin before 2.8.10 does not sanitize and escape some parameters, which could allow administrators in multisite WordPress configurations to perform Cross-Site Scripting attacks
- Product
- System Dashboard
- Fixed in
- 2.8.10
- What to do
- Update System Dashboard to 2.8.10 or newer.
Mar 19, 2024Data was not properly sanitized when decoding a QUIC ACK frame; this could have led to unrestricted memory consumption and a crash.CVE-2024-2613 · Computers, phones & browsers · Mozilla · reported by security@mozilla.orgHigh 7.5
Data was not properly sanitized when decoding a QUIC ACK frame; this could have led to unrestricted memory consumption and a crash. This vulnerability affects Firefox < 124.
- Product
- Firefox
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbugzilla.mozilla.orgmozilla.org
Mar 18, 2024Scalable Vector Graphics (SVG): Does not sanitize uploaded SVG filesCVE-2023-7085 · WordPress plugins & themes · reported by WPScanMedium 5.4
The Scalable Vector Graphics (SVG) WordPress plugin through 3.4 does not sanitize uploaded SVG files, which could allow users with a role as low as Author to upload a malicious SVG containing XSS payloads.
- Product
- Scalable Vector Graphics (SVG)
- Affected
- up to 3.4
- What to do
- Affects up to 3.4. Update Scalable Vector Graphics (SVG) to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Mar 18, 2024In OpenStack Murano through 16.0.0, when YAQL before 3.0.0 is used, the Murano service's MuranoPL extension to the YAQL language fails to sanitize the supplied CVE-2024-29156 · Other software · Openstack · reported by MITREMedium 6.5
In OpenStack Murano through 16.0.0, when YAQL before 3.0.0 is used, the Murano service's MuranoPL extension to the YAQL language fails to sanitize the supplied environment, leading to potential leakage of sensitive service account information.
- Product
- Murano
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordlaunchpad.netopendev.org
Mar 13, 2024In FileCatalyst Direct 3.8.8 and earlier through 3.8.6, the web server does not properly sanitize illegal characters in a URL which is then displayed on a subseCVE-2024-25155 · Other software · Fortra · reported by df4dee71-de3a-4139-9588-11b62fe6c0ffHigh 7.2
In FileCatalyst Direct 3.8.8 and earlier through 3.8.6, the web server does not properly sanitize illegal characters in a URL which is then displayed on a subsequent error page. A malicious actor could craft a URL which would then execute arbitrary code within an HTML script tag.
- Product
- FileCatalyst
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordfilecatalyst.softwarefortra.com
Mar 11, 2024Photos and Files Contest Gallery: Does not sanitize and escape some parametersCVE-2024-1487 · WordPress plugins & themes · reported by WPScanMedium 5.4
The Photos and Files Contest Gallery WordPress plugin before 21.3.1 does not sanitize and escape some parameters, which could allow users with a role as low as author to perform Cross-Site Scripting attacks.
- Product
- Photos and Files Contest Gallery
- Fixed in
- 21.3.1
- What to do
- Update Photos and Files Contest Gallery to 21.3.1 or newer.
Mar 6, 2024Jenkins iceScrum Plugin 1.1.6 and earlier does not sanitize iceScrum project URLs on build views, resulting in a stored cross-site scripting (XSS) vulnerabilityCVE-2024-28160 · Websites & servers · Jenkins Project · reported by jenkinsci-cert@googlegroups.comHigh 8.8
Jenkins iceScrum Plugin 1.1.6 and earlier does not sanitize iceScrum project URLs on build views, resulting in a stored cross-site scripting (XSS) vulnerability exploitable by attackers able to configure jobs.
- Product
- Jenkins iceScrum Plugin
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordopenwall.comjenkins.io
Mar 6, 2024Jenkins GitBucket Plugin 0.8 and earlier does not sanitize Gitbucket URLs on build views, resulting in a stored cross-site scripting (XSS) vulnerability exploitCVE-2024-28157 · Websites & servers · Jenkins Project · reported by jenkinsci-cert@googlegroups.comHigh 8
Jenkins GitBucket Plugin 0.8 and earlier does not sanitize Gitbucket URLs on build views, resulting in a stored cross-site scripting (XSS) vulnerability exploitable by attackers able to configure jobs.
- Product
- Jenkins GitBucket Plugin
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordopenwall.comjenkins.io
Mar 6, 2024Jenkins HTML Publisher Plugin 1.16 through 1.32 (both inclusive) does not properly sanitize input, allowing attackers with Item/Configure permission to implemenCVE-2024-28149 · Websites & servers · Jenkins Project · reported by jenkinsci-cert@googlegroups.comMedium 6.5
Jenkins HTML Publisher Plugin 1.16 through 1.32 (both inclusive) does not properly sanitize input, allowing attackers with Item/Configure permission to implement cross-site scripting (XSS) attacks and to determine whether a path on the Jenkins controller file system exists.
- Product
- Jenkins HTML Publisher Plugin
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordopenwall.comjenkins.io
Feb 29, 2024Mattermost version 8.1.x before 8.1.9 fails to sanitize data associated with permalinks when a plugin updates an ephemeral post, allowing an authenticated attacCVE-2024-1952 · Other software · Mattermost · reported by responsibledisclosure@mattermost.comLow 3.1
Mattermost version 8.1.x before 8.1.9 fails to sanitize data associated with permalinks when a plugin updates an ephemeral post, allowing an authenticated attacker who can control the ephemeral post update to access individual posts' contents in channels they are not a member of.
- Product
- Mattermost
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmattermost.commattermost.com
Feb 29, 2024Mattermost versions 8.1.x before 8.1.9, 9.2.x before 9.2.5, and 9.3.0 fail to sanitize the metadata on posts containing permalinks under specific conditions, whCVE-2024-1942 · Other software · Mattermost · reported by responsibledisclosure@mattermost.comMedium 4.3
Mattermost versions 8.1.x before 8.1.9, 9.2.x before 9.2.5, and 9.3.0 fail to sanitize the metadata on posts containing permalinks under specific conditions, which allows an authenticated attacker to access the contents of individual posts in channels they are not a member of.
- Product
- Mattermost
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmattermost.commattermost.com
Feb 24, 2024Versions of the package sanitize-html before 2.12.1 are vulnerable to Information Exposure when used on the backend and with the style attribute allowed, allowiCVE-2024-21501 · Other software · apostrophecms · reported by report@snyk.ioMedium 5.3
Versions of the package sanitize-html before 2.12.1 are vulnerable to Information Exposure when used on the backend and with the style attribute allowed, allowing enumeration of files in the system (including project dependencies). An attacker could exploit this vulnerability to gather details about the file system structure and dependencies of the targeted server.
- Product
- sanitize-html
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordgist.github.comgithub.com
Feb 22, 2024### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`ChoCVE-2024-26152 · Other software · HumanSignal · reported by GitHubMedium 4.7
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 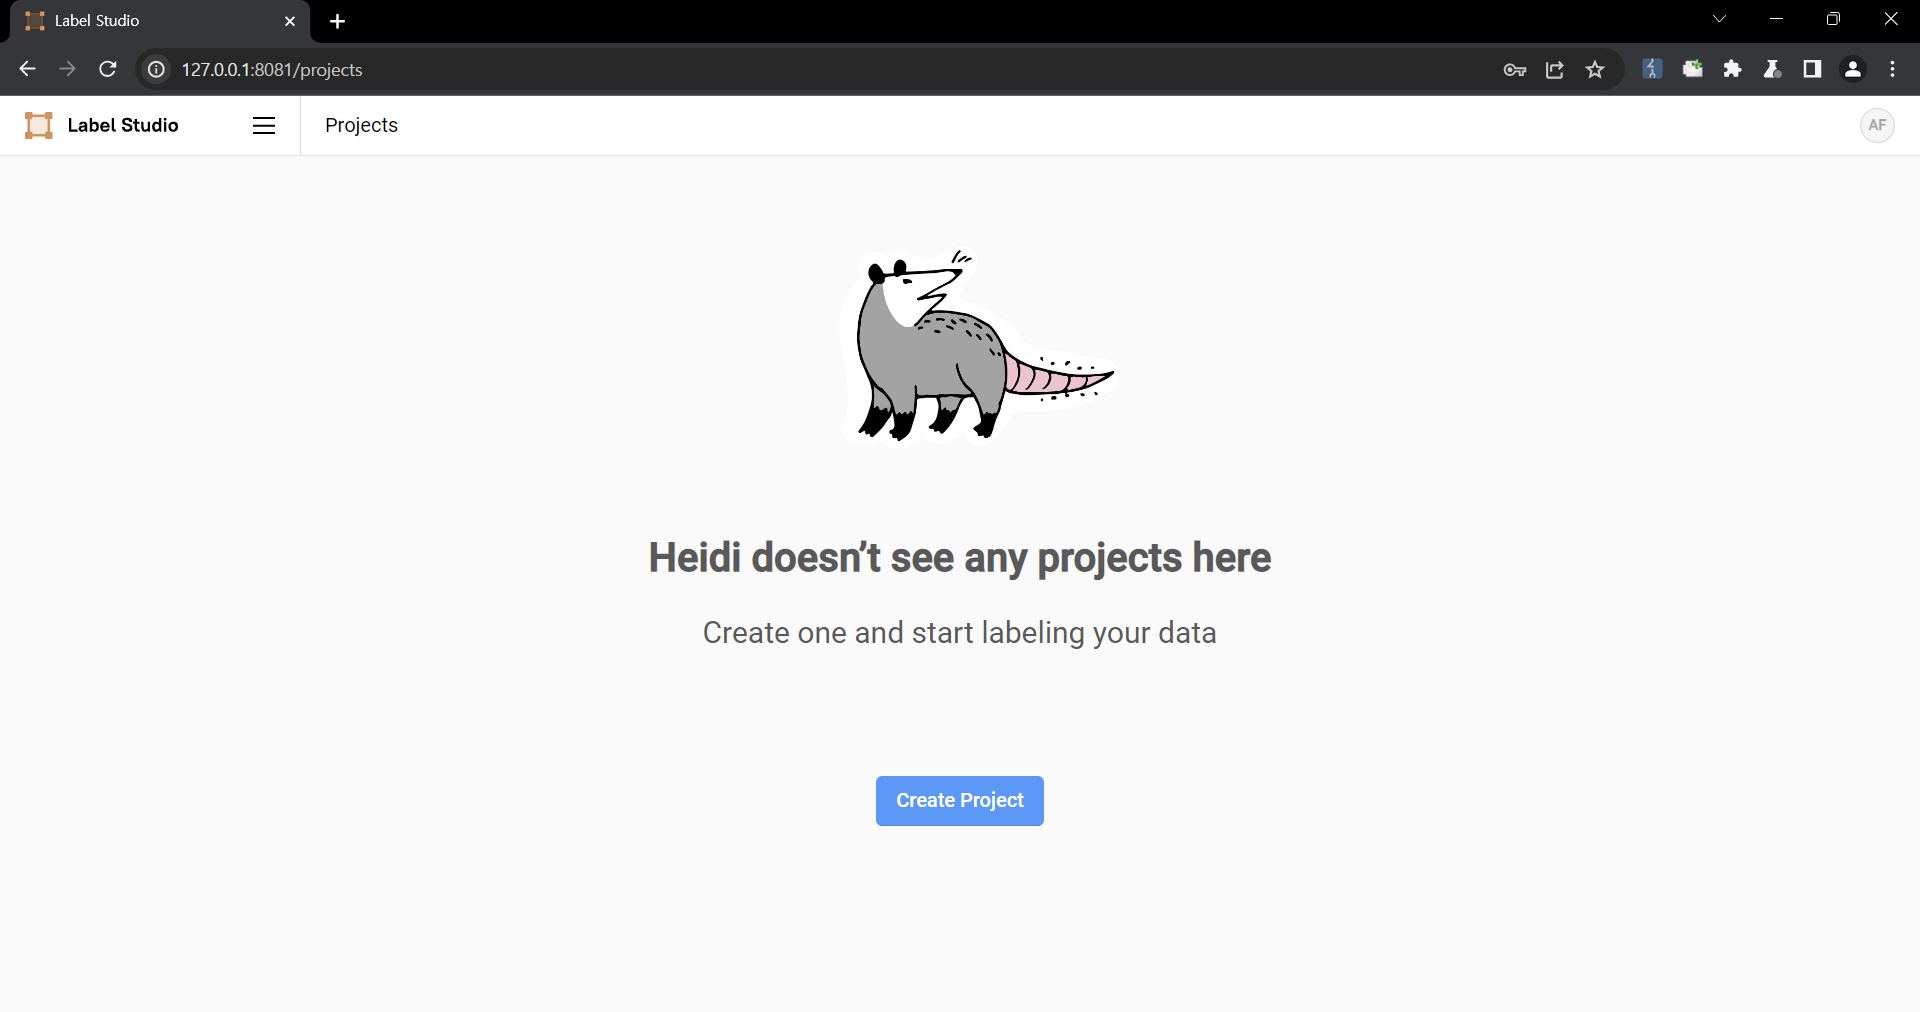 2. Upload a file containing the payload using the "Upload Files" function. 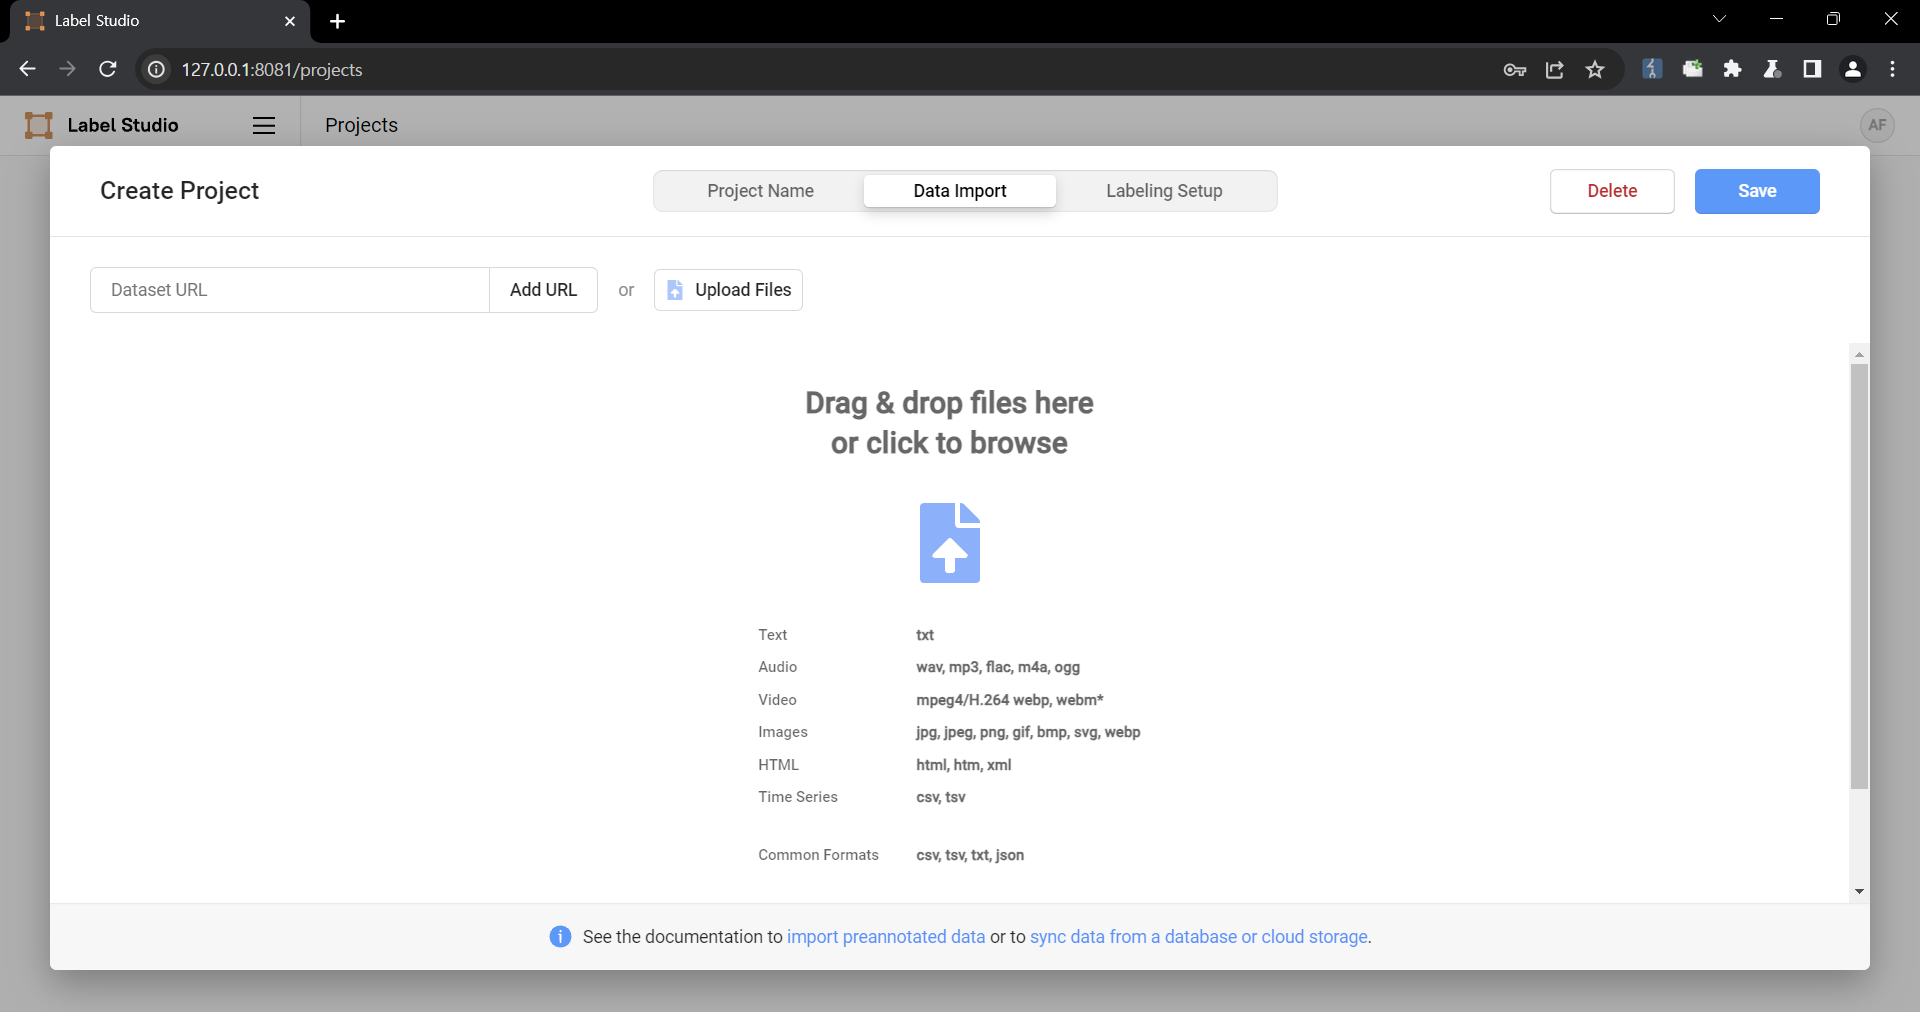 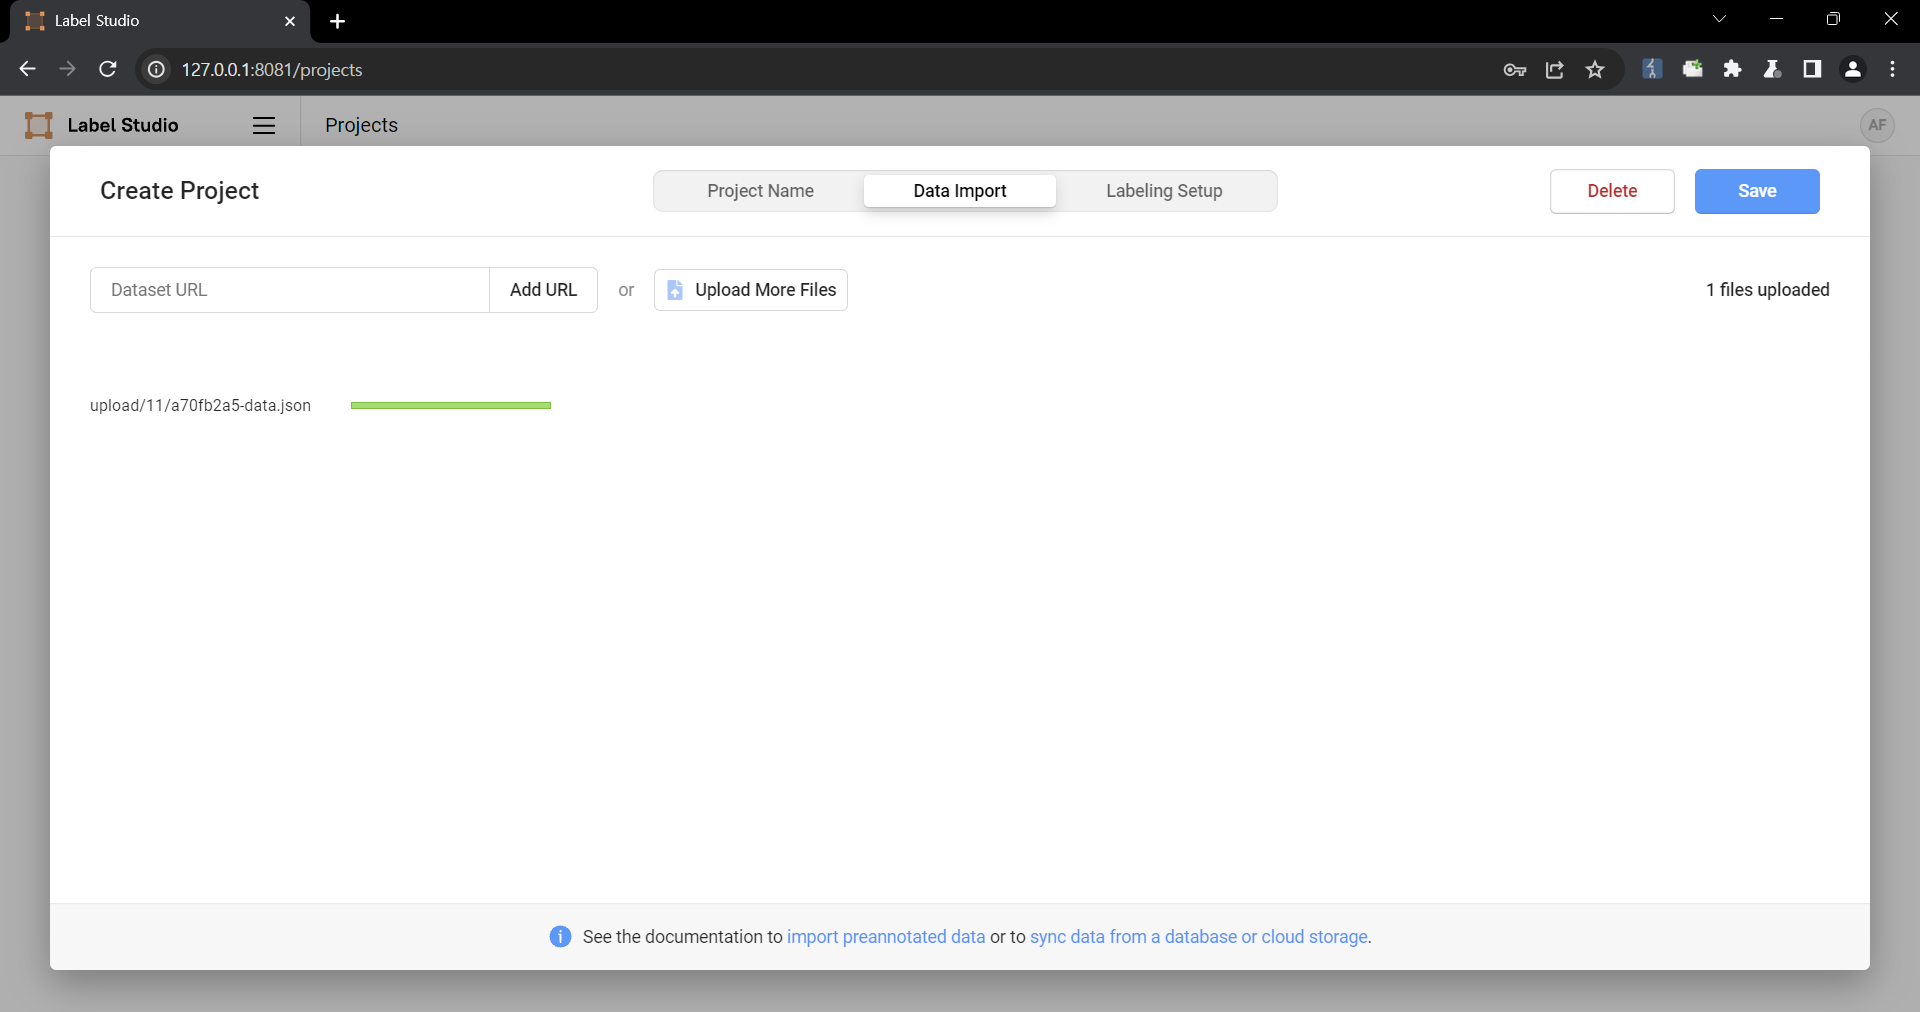 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 20, 2024Cross Site Scripting vulnerability in the sanitize function in Enhancesoft osTicket 1.18.0 allows a remote attacker to escalate privileges via a crafted supportCVE-2023-46967 · Other software · enhancesoft · reported by MITREMedium 6.1
Cross Site Scripting vulnerability in the sanitize function in Enhancesoft osTicket 1.18.0 allows a remote attacker to escalate privileges via a crafted support ticket.
- Product
- osticket
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordsonarsource.comsonarsource.com
Feb 15, 2024In sanitizeSbn of NotificationManagerService.java, there is a possible way to launch an activity from the background due to BAL Bypass.CVE-2023-40106 · Computers, phones & browsers · Google · reported by security@android.comHigh 7.8
In sanitizeSbn of NotificationManagerService.java, there is a possible way to launch an activity from the background due to BAL Bypass. This could lead to local escalation of privilege with no additional execution privileges needed. User interaction is not needed for exploitation.
- Product
- Android
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordandroid.googlesource.comsource.android.com
Feb 12, 2024MapPress Maps for: Does not sanitize and escape the map titleCVE-2024-0420 · WordPress plugins & themes · reported by WPScanMedium 5.4
The MapPress Maps for WordPress plugin before 2.88.15 does not sanitize and escape the map title when outputting it back in the admin dashboard, allowing Contributors and above roles to perform Stored Cross-Site Scripting attacks
- Product
- MapPress Maps for
- Fixed in
- 2.88.15
- What to do
- Update MapPress Maps for to 2.88.15 or newer.
Feb 12, 2024User ID references at mentions in document comments were not correctly sanitized.CVE-2023-41703 · Other software · Open-Xchange GmbH · reported by security@open-xchange.comMedium 6.1
User ID references at mentions in document comments were not correctly sanitized. Script code could be injected to a users session when working with a malicious document. Please deploy the provided updates and patch releases. User-defined content like comments and mentions are now filtered to avoid potentially malicious content. No publicly available exploits are known.
- Product
- OX App Suite
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddocumentation.open-xchange.comsoftware.open-xchange.com
Feb 3, 2024The Jinja templating in Logpoint SIEM 6.10.0 through 7.x before 7.3.0 does not correctly sanitize log data being displayed when using a custom Jinja template inCVE-2023-49950 · Other software · Logpoint · reported by MITREMedium 5.4
The Jinja templating in Logpoint SIEM 6.10.0 through 7.x before 7.3.0 does not correctly sanitize log data being displayed when using a custom Jinja template in the Alert view. A remote attacker can craft a cross-site scripting (XSS) payload and send it to any system or device that sends logs to the SIEM. If an alert is created, the payload will execute upon the alert data being viewed with that template, which can lead to sensitive data disclosure.
- Product
- Siem
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordgithub.comservicedesk.logpoint.com
Jan 29, 2024Easy SVG Allow: Does not sanitize uploaded SVG filesCVE-2023-7089 · WordPress plugins & themes · reported by WPScanMedium 5.4
The Easy SVG Allow WordPress plugin through 1.0 does not sanitize uploaded SVG files, which could allow users with a role as low as Author to upload a malicious SVG containing XSS payloads.
- Product
- Easy SVG Allow
- Affected
- up to 1.0
- What to do
- Affects up to 1.0. Update Easy SVG Allow to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Jan 24, 2024Jenkins Matrix Project Plugin 822.v01b_8c85d16d2 and earlier does not sanitize user-defined axis names of multi-configuration projects, allowing attackers with CVE-2024-23900 · Websites & servers · Jenkins Project · reported by jenkinsci-cert@googlegroups.comMedium 4.3
Jenkins Matrix Project Plugin 822.v01b_8c85d16d2 and earlier does not sanitize user-defined axis names of multi-configuration projects, allowing attackers with Item/Configure permission to create or replace any config.xml files on the Jenkins controller file system with content not controllable by the attackers.
- Product
- Jenkins Matrix Project Plugin
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordopenwall.comjenkins.io
Jan 22, 2024In Splunk Enterprise for Windows versions below 9.0.8 and 9.1.3, Splunk Enterprise does not correctly sanitize path input data.CVE-2024-23678 · Other software · Splunk · reported by prodsec@splunk.comHigh 7.5
In Splunk Enterprise for Windows versions below 9.0.8 and 9.1.3, Splunk Enterprise does not correctly sanitize path input data. This results in the unsafe deserialization of untrusted data from a separate disk partition on the machine. This vulnerability only affects Splunk Enterprise for Windows.
- Product
- Splunk Enterprise
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordadvisory.splunk.comresearch.splunk.com
Jan 17, 2024Track The Click: Does not properly sanitize query parameters to the stats REST endpoint before using them in a database queryCVE-2023-5041 · WordPress plugins & themes · reported by WPScanHigh 8.8
The Track The Click WordPress plugin before 0.3.12 does not properly sanitize query parameters to the stats REST endpoint before using them in a database query, allowing a logged in user with an author role or higher to perform time based blind SQLi attacks on the database.
- Product
- Track The Click
- Fixed in
- 0.3.12
- What to do
- Update Track The Click to 0.3.12 or newer.
Jan 16, 2024ArtPlacer Widget: Does not sanitize and escape the "id" parameter before submitting the queryCVE-2023-6373 · WordPress plugins & themes · reported by WPScanHigh 8.8
The ArtPlacer Widget WordPress plugin before 2.20.7 does not sanitize and escape the "id" parameter before submitting the query, leading to a SQLI exploitable by editors and above. Note: Due to the lack of CSRF check, the issue could also be exploited via a CSRF against a logged editor (or above)
- Product
- ArtPlacer Widget
- Fixed in
- 2.20.7
- What to do
- Update ArtPlacer Widget to 2.20.7 or newer.
Jan 16, 2024EventON WordPress plugin before 4.5.5, EventON: Does not sanitize and escape some of its settingsCVE-2023-6005 · WordPress plugins & themes · reported by WPScanMedium 4.8
The EventON WordPress plugin before 4.5.5, EventON WordPress plugin before 2.2.7 does not sanitize and escape some of its settings, which could allow high privilege users such as admin to perform Stored Cross-Site Scripting attacks even when the unfiltered_html capability is disallowed (for example in multisite setup).
- Product
- EventON WordPress plugin before 4.5.5, EventON
- Fixed in
- 4.5.5
- What to do
- Update EventON WordPress plugin before 4.5.5, EventON to 4.5.5 or newer.
Jan 16, 2024Staff / Employee Business Directory for Active Directory: Does not sanitize and escape data returned from the LDAP server before rendering it in the pageCVE-2023-4757 · WordPress plugins & themes · reported by WPScanMedium 5.4
The Staff / Employee Business Directory for Active Directory WordPress plugin before 1.2.3 does not sanitize and escape data returned from the LDAP server before rendering it in the page, allowing users who can control their entries in the LDAP directory to inject malicious javascript which could be used against high-privilege users such as a site admin.
- Product
- Staff / Employee Business Directory for Active Directory
- Fixed in
- 1.2.3
- What to do
- Update Staff / Employee Business Directory for Active Directory to 1.2.3 or newer.
Jan 16, 2024WP Best Quiz: Does not sanitize and escape some parametersCVE-2022-3739 · WordPress plugins & themes · reported by WPScanMedium 5.4
The WP Best Quiz WordPress plugin through 1.0 does not sanitize and escape some parameters, which could allow users with a role as low as Author to perform Cross-Site Scripting attacks.
- Product
- WP Best Quiz
- Affected
- up to 1.0
- What to do
- Affects up to 1.0. Update WP Best Quiz to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Jan 16, 2024Slide Anything: Does not properly sanitize or escape the slide title before outputting it in the admin pagesCVE-2022-2413 · WordPress plugins & themes · reported by WPScanMedium 5.4
The Slide Anything WordPress plugin before 2.3.47 does not properly sanitize or escape the slide title before outputting it in the admin pages, allowing a logged in user with roles as low as Author to inject a javascript payload into the slide title even when the unfiltered_html capability is disabled.
- Product
- Slide Anything
- Fixed in
- 2.3.47
- What to do
- Update Slide Anything to 2.3.47 or newer.
Where this comes from: the exploited list is CISA’s Known Exploited Vulnerabilities catalog. Everything else is the whole National Vulnerability Database, where each record is published by the team that found the bug (Wordfence, Patchstack, WPScan, the vendors themselves and others); we show who. Exploit odds are FIRST’s EPSS, updated daily. Titles and categories are ours, so check the linked record before acting on a detail. For a write-up of the big ones, see our advisories. Every vendor, and every WordPress plugin and theme with a recorded flaw, also has its own page. All of it is free to reuse as JSON, CSV or RSS.
Weekly security brief
The flaws that hit local websites, every Friday.
One short email: what got exploited this week, which WordPress plugins broke, and what to check. Unsubscribe in one click.
Tell us what you're building.
A website, your marketing, a security check, an app, or the thing you've been running out of a spreadsheet for three years. A few lines is plenty.
Not ready to talk yet? Run the free website check and see what Google sees.